Old PCs in Storage: The Data Breach Risk Most Businesses Overlook
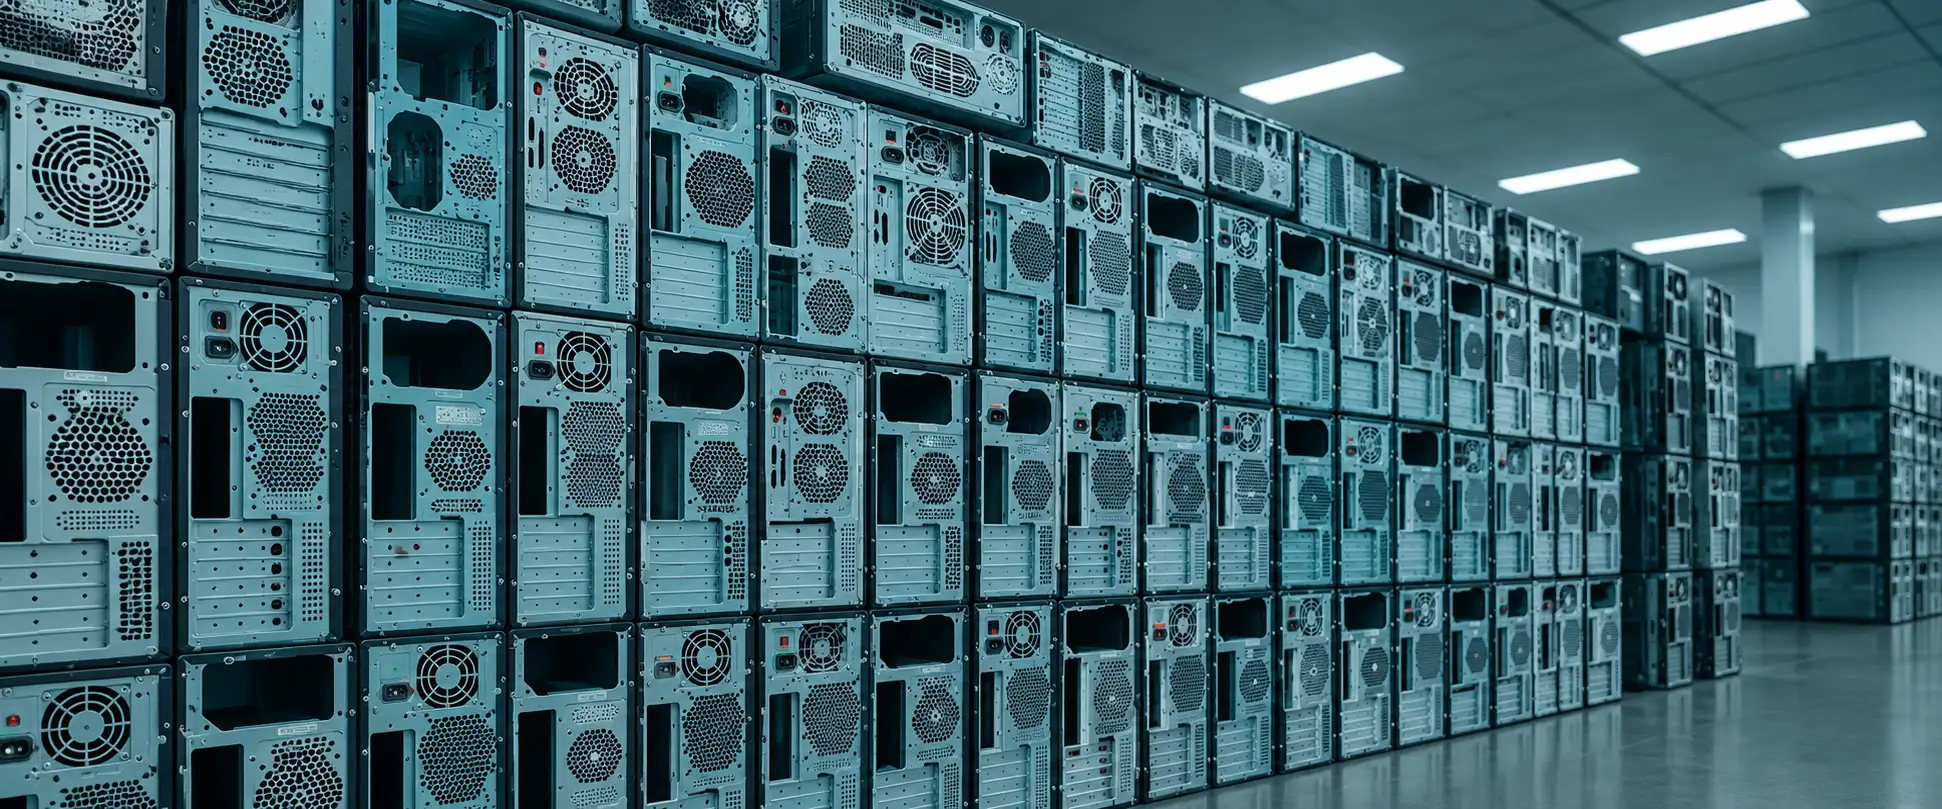
Most data breaches involving retired IT equipment don’t start with a hacker — they start with a forgotten PC. Office moves and IT refreshes routinely leave old desktops, laptops and drives sitting in storerooms, cupboards or off-site units, unmanaged and unencrypted, long after anyone stopped thinking about them. A device doesn’t need to be switched on to be a risk: if it still holds data, it’s still exposed. Here’s why that happens, what regulators expect you to be able to prove, and how secure IT disposal closes the gap.
At a Glance
- A factory reset or reformat does not securely erase data — recovery tools can often still retrieve information from HDDs and SSDs afterwards.
- Data destruction should be carried out to a recognised standard such as NIST 800-88 (Clear or Purge), with a serialised certificate issued for every device.
- Free collection is available for 20 or more qualifying business items under four years old, across England, Scotland and Wales.
- Every collection runs on GPS-tracked vehicles with BS 7858:2019 security-vetted staff, with a full compliance pack delivered within 5 working days.
- Computer IT Disposals is ISO 9001:2015 and ISO 14001:2015 certified, ICO registered (ZA246798) and Cyber Essentials Plus certified.
Why Old, Unused PCs Are a Hidden Data Risk
Retired computers fall out of scrutiny the moment they’re switched off. While a device is in active use, it typically sits behind firewalls, access controls and monitoring. Once it’s unplugged and put in a cupboard, none of that applies — but the data inside it hasn’t gone anywhere. Client records, trade secrets, intellectual property and login credentials can all still be sitting on a hard drive that hasn’t been touched in years.
This usually happens for mundane reasons rather than negligence. Office relocations are the most common trigger: in the rush to move, old kit gets boxed up “to deal with later” and quietly becomes permanent storage. IT refreshes create the same problem on a rolling basis, as replaced devices pile up faster than anyone gets round to disposing of them properly.
The Factory Reset Myth
The most common assumption we come across is that a factory reset or a reformatted drive counts as data destruction. It doesn’t. Both actions typically remove the pointers to files rather than the data itself — recovery software can often retrieve it afterwards. This applies equally to HDDs and SSDs, and it isn’t limited to computers: printers, routers and even some monitors hold onboard memory that can retain data too.
What Actually Puts Your Business at Risk
A few patterns come up repeatedly in businesses that don’t realise they have a problem:
- No inventory of retired equipment — if nobody can say how many old PCs the business currently holds, nobody can account for what’s on them.
- Undocumented storage — devices sitting in cupboards, storerooms or off-site units with no access log or clear ownership.
- No chain-of-custody record — no documented trail of who handled a device, and when, between retirement and destruction.
- No destruction certificate per device — a general statement that “equipment was recycled” isn’t evidence a regulator or auditor will accept.
- Unclear ownership — disposal responsibility split loosely across IT, facilities and compliance often means no one actually owns it.
- “Free” recycling with no paperwork — a free collection isn’t a problem in itself, but one with no documentation usually means the equipment is being resold with the data still on it.
What Regulators Expect You to Be Able to Prove
Under UK GDPR and the Data Protection Act 2018, your business remains responsible for personal data even once retired equipment has left the building — right up until you can evidence it was properly destroyed. “We used a recycler” isn’t evidence on its own; a certificate tied to specific serial numbers and destruction dates is. That bar has also moved recently: the NCSC’s CAS-S data-sanitisation certification scheme closed in January 2026, replaced by an assurance model delivered through Cyber Resilience Test Facilities — another sign that buyers are expected to actively verify a provider’s standards rather than take a certificate at face value.
How Secure IT Disposal Actually Works
Here’s what a properly documented process looks like in practice:
- Controlled collection — on GPS-tracked vehicles, by BS 7858:2019 security-vetted staff, so equipment never passes through unvetted hands. Free collectionis available for 20 or more qualifying items under four years old.
- Serial-level asset tracking — every device logged individually and tracked through to disposition, not counted only as part of a bulk pickup.
- Certified data destruction — data wiped to NIST 800-88, or physically destroyed via hard drive shredding where destruction is required, rather than reused with only a factory reset applied.
- Documented chain of custody — a continuous, auditable record from collection to certificate.
- WEEE and GDPR compliance — processed under our WEEE recycling programme, with 100% diverted from landfill.
- Audit-ready documentation — a serialised Data Destruction Certificate and WEEE Certificate issued within 5 working days, so the paperwork exists before anyone asks for it.
What to Do If This Sounds Like Your Business
The fix is rarely complicated — it just needs turning into a defined process rather than an occasional clear-out. Start with a simple inventory of what’s actually in storage, assign clear ownership for disposal (even if it’s just “IT signs off, compliance reviews”), and route anything retired through a provider who can evidence the full chain of custody, not just collect it.
We’ve helped organisations clear a significant backlog of stored IT equipment under exactly this kind of process — see the case study for how a full estate clearance and secure data destruction project runs in practice.
Turning a Storage Room Risk Into a Closed File
A cupboard of retired PCs isn’t a data breach waiting to happen if it’s handled properly — it’s just equipment that hasn’t been processed yet. Treated as a standard part of your IT asset lifecycle rather than an afterthought, disposal becomes a closed file: serial numbers logged, certificates issued, nothing left unaccounted for.
We collect from businesses across England, Scotland and Wales, including London, Birmingham, Manchester, Nottingham and Bristol. Our data destruction and asset management processes are built to give you exactly the kind of evidence a regulator, auditor or insurer would ask for — full certifications are listed on our licenses page.
Booking Form
Free collection available for qualifying items · certificates within 5 working days · 100% diverted from landfill.